Canada's Bill C-22: Dhillon backs lawful access; Simons warns of security risks
Baltej Dhillon defends Bill C-22's lawful-access capability framework. Paula Simons, Yuen Pau Woo and Robert Diab question its privacy, cybersecurity and oversight safeguards. The House-passed text caps metadata retention at six months. As of October 24, 2026, it was before a Senate committee.
Case period:
Published by The Dispute Index editorial teamPublished Updated
Overview
Senator Baltej Dhillon defends the lawful-access framework in Part 2 of Bill C-22. Senators Paula Simons and Yuen Pau Woo question its privacy, cybersecurity and oversight safeguards. The House-passed text lets the federal cabinet require designated providers to keep categories of metadata for up to six months. As of October 24, 2026, the bill was before a Senate committee and was not law.
Read the full background
Part 2 of Bill C-22 (clause 41) would enact the Supporting Authorized Access to Information Act; the section numbers here refer to that Act. In the House-passed text, the federal cabinet could require classes of core providers to build and maintain technical capabilities and to retain categories of metadata for up to six months (section 5(2)). The schedule that lists those classes is empty, and cabinet would add classes by regulation (section 5(1)). Retention rules could not require information that would reveal the content of communications, a person's web browsing history or social media activity, and cabinet must be satisfied that each category is essential to criminal investigations or to the work of the Canadian Security Intelligence Service (CSIS) (sections 5(4) and 5(4.1)). The Minister of Public Safety could also order any electronic service provider to meet such obligations for up to two years, and an order is not valid until the Intelligence Commissioner approves it (sections 7(1) and 7(2)). Bill C-22, as passed by the House of Commons (opens in a new tab)
Part 2 states that its purpose is to help providers facilitate access powers conferred under the Criminal Code and the CSIS Act, and it leaves those powers in place (sections 2(1), 2(2) and 3). It says the capability regulations cannot confer an authority to access personal information about a provider's users (section 5(6)). A provider need not comply with a regulation or order that would introduce a systemic vulnerability or keep it from fixing one (sections 5(5), 7(5) and 24(2.1)). Its obligations are not to be read as compelling a provider to decrypt a user's encrypted information, or to enable decryption, unless the provider supplied the encryption and holds the means to decrypt it (section 2(4)). The government says these safeguards protect encryption and keep a warrant or production order as the route to personal information. Critics question whether they adequately address the risks of compelled capabilities and retention. Government of Canada (opens in a new tab)
The House of Commons passed the bill with committee amendments on June 18, 2026. Compared with the text introduced on March 12, the amendments cut the retention ceiling from one year to six months and revised the definition of a systemic vulnerability. They also added the decryption clause, the essential-category test and a two-year limit on ministerial orders. The Senate gave the bill second reading on October 22, 2026 and referred it to its Standing Committee on National Security, Defence and Veterans Affairs. As of October 24, 2026, the committee had not reported and the bill had not received royal assent. Part 2 would come into force on a date the federal cabinet sets (clause 47). LEGISinfo (opens in a new tab) Bill C-22, first reading (opens in a new tab)
Robert Diab's June 19 analysis considers the Commons amendments. The Senate debate of October 8, the first day of second-reading debate, contains arguments from Dhillon, Simons and Woo.
People in this case
 Baltej Singh DhillonDirectly involved
 Yuen Pau WooDirectly involved
Timeline
5 timeline entries on this page. Dates: March 12, 2026 to October 22, 2026
March 2026
The government introduces Bill C-22 in the House of Commons
Public Safety Minister Gary Anandasangaree introduces the bill. As introduced, Part 2 would let the federal cabinet require core providers to keep categories of metadata for up to one year.
[01]Bill C-22, Lawful Access Act, 2026, as introduced in the House of Commons
As introduced, Part 2 let the federal cabinet require core providers to retain categories of metadata for up to one year (section 5(2)(d)). It defined a systemic vulnerability as one that creates a substantial risk of unauthorized access, and it set no maximum length for ministerial orders (section 7(1)). The House of Commons public safety committee amended these provisions before the House passed the bill on June 18, 2026.
Bill C-22, Lawful Access Act, 2026, as introduced in the House of CommonsPart 2, clause 41: new Act ss. 2(1) (systemic vulnerability), 5(2)(d) and 7(1)[02]LEGISinfo: Bill C-22 (45th Parliament, 1st Session), An Act respecting lawful access
LEGISinfo records first reading in the House of Commons on March 12, 2026, committee amendments and third reading on June 18, 2026, and Senate second reading and referral to the Standing Senate Committee on National Security, Defence and Veterans Affairs on October 22, 2026. When we checked it on October 24, 2026, the bill was at consideration in committee in the Senate, the committee stage showed no activity, and the bill had not received royal assent.
LEGISinfo: Bill C-22 (45th Parliament, 1st Session), An Act respecting lawful accessBill status; House of Commons and Senate stages; publications
June 2026
The House of Commons passes Bill C-22 with committee amendments
The public safety committee reports the bill with amendments, and the House passes it at third reading the same day. The passed text caps metadata retention at six months, limits decryption obligations and revises the definition of a systemic vulnerability.
[03]Bill C-22, Lawful Access Act, 2026, as passed by the House of Commons
Part 2 of the House-passed text enacts the Supporting Authorized Access to Information Act. Section 5(2) lets the federal cabinet set capability and metadata-retention obligations for core providers, with retention capped at six months. Section 7 lets the Minister of Public Safety order any electronic service provider to meet such obligations for up to two years, once the Intelligence Commissioner approves the order. Sections 5(5), 7(5) and 24(2.1) excuse compliance that would introduce a systemic vulnerability, and section 2(4) limits decryption obligations.
Bill C-22, Lawful Access Act, 2026, as passed by the House of CommonsPart 2, clause 41: new Act ss. 2(1)-(4), 3, 5(1)-(6), 7(1)-(5), 24(2.1) and schedule; clauses 47 and 48[01]Bill C-22, Lawful Access Act, 2026, as introduced in the House of Commons
As introduced, Part 2 let the federal cabinet require core providers to retain categories of metadata for up to one year (section 5(2)(d)). It defined a systemic vulnerability as one that creates a substantial risk of unauthorized access, and it set no maximum length for ministerial orders (section 7(1)). The House of Commons public safety committee amended these provisions before the House passed the bill on June 18, 2026.
Bill C-22, Lawful Access Act, 2026, as introduced in the House of CommonsPart 2, clause 41: new Act ss. 2(1) (systemic vulnerability), 5(2)(d) and 7(1)[02]LEGISinfo: Bill C-22 (45th Parliament, 1st Session), An Act respecting lawful access
LEGISinfo records first reading in the House of Commons on March 12, 2026, committee amendments and third reading on June 18, 2026, and Senate second reading and referral to the Standing Senate Committee on National Security, Defence and Veterans Affairs on October 22, 2026. When we checked it on October 24, 2026, the bill was at consideration in committee in the Senate, the committee stage showed no activity, and the bill had not received royal assent.
LEGISinfo: Bill C-22 (45th Parliament, 1st Session), An Act respecting lawful accessBill status; House of Commons and Senate stages; publicationsDiab publishes an analysis of the Commons amendments
Source release
He questions whether the changed encryption and retention provisions resolve the privacy concerns.
[04]Robert Diab examines Bill C-22 after the Commons amendments
Diab considers the amended text and questions whether its safeguards resolve privacy concerns.
Robert Diab examines Bill C-22 after the Commons amendmentsEncryption and metadata-retention sections
October 2026
Senators debate capability obligations and safeguards
Dhillon defends the framework; Simons and Woo question privacy, security and oversight.
[05]Senate debate on Bill C-22's lawful-access powers
The debate contains competing evaluations of capability obligations, metadata retention, cybersecurity and oversight.
Senate debate on Bill C-22's lawful-access powersBill C-22 second reading: Dhillon, Simons and Woo speechesThe Senate passes Bill C-22 at second reading and refers it to committee
The bill goes to the Standing Senate Committee on National Security, Defence and Veterans Affairs. As of October 24, 2026, the committee had not reported and the bill had not received royal assent.
[02]LEGISinfo: Bill C-22 (45th Parliament, 1st Session), An Act respecting lawful access
LEGISinfo records first reading in the House of Commons on March 12, 2026, committee amendments and third reading on June 18, 2026, and Senate second reading and referral to the Standing Senate Committee on National Security, Defence and Veterans Affairs on October 22, 2026. When we checked it on October 24, 2026, the bill was at consideration in committee in the Senate, the committee stage showed no activity, and the bill had not received royal assent.
LEGISinfo: Bill C-22 (45th Parliament, 1st Session), An Act respecting lawful accessBill status; House of Commons and Senate stages; publications[06]Senate of Canada: Progress of legislation, 1st Session, 45th Parliament
The Senate's progress table, dated October 22, 2026, records first reading of Bill C-22 in the Senate on June 18, 2026 and second reading on October 22, 2026, with referral to the National Security, Defence and Veterans Affairs committee. It lists no committee report, third reading or royal assent for the bill.
Senate of Canada: Progress of legislation, 1st Session, 45th ParliamentGovernment bills (House of Commons): C-22
Response record
Responses
Choose one response filter, or select All responses to see the full record.
3 matching responses. Newest first.
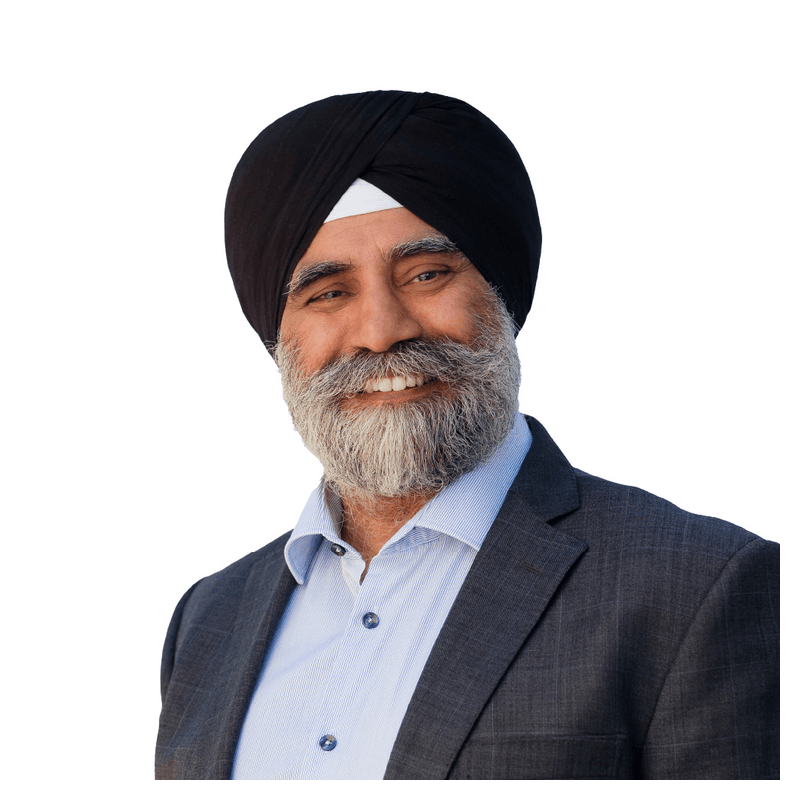
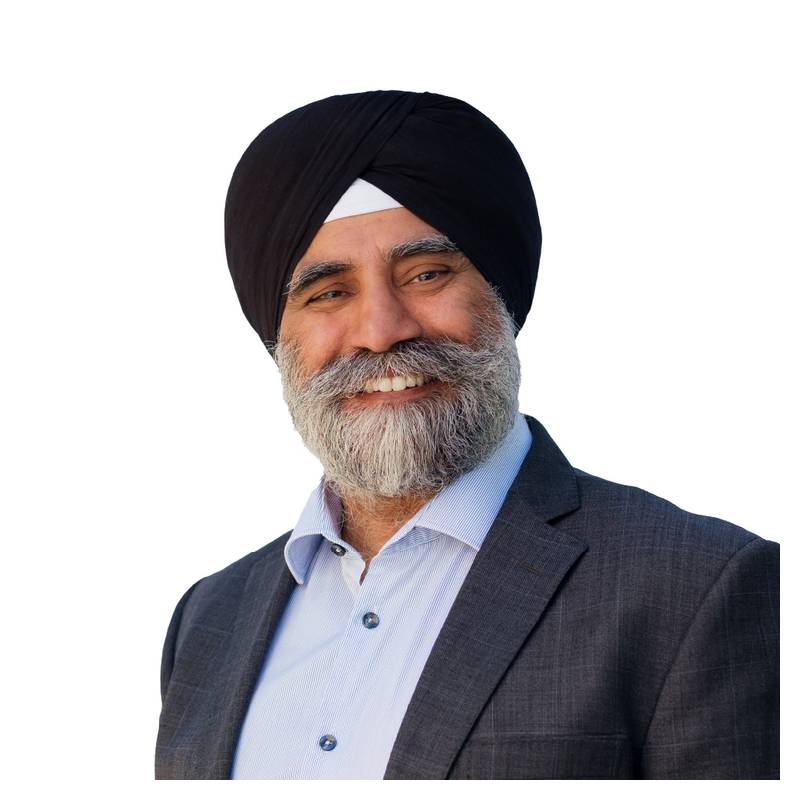 Baltej Singh DhillonCanadian senator for British Columbia and sponsor of Bill C-22Directly involved
Before this statement
Dhillon compares Canada's proposed framework with those of other Five Eyes countries.
"Our responsibility is to build a Canadian framework that responds to genuine investigative needs and complies with our Charter, our legal traditions and our commitment to cybersecurity. Law enforcement and the Canadian Security Intelligence Service, or CSIS, must be able to adapt, but that adaptability must remain bound by law, independent authorization and meaningful review. Bill C-22 provides a framework for that work."
Defended or excusedCase context: Canada's Bill C-22: Dhillon backs lawful access; Simons warns of security risks
Full statement and sources
Dhillon argues that Bill C-22 provides a framework for investigative powers bounded by law, independent authorization and review.
After the statement
He says Canadians expect both effective security measures and protection for privacy, cybersecurity and Charter rights.
Senate debate on Bill C-22's lawful-access powersBill C-22 second reading: Dhillon, Simons and Woo speechesCanada explains amendments and safeguards in Bill C-22Part 2; safeguards; metadata retentionWhy this label?
The case concerns Bill C-22's compulsory lawful-access capabilities and retention framework. Dhillon endorses the bill as a framework for investigative powers governed by legal limits, independent authorization and review.
This label describes the statement's response within the context above.
Paula SimonsCanadian senator for AlbertaDirectly involved Before this statement
Simons argues that an access route built for investigators could also be used by hostile actors.
"no way to create a secret passage"
CondemnedCase context: Canada's Bill C-22: Dhillon backs lawful access; Simons warns of security risks
Full statement and sources
Simons criticizes the security consequences of compulsory capabilities.
After the statement
She argues that weakening encryption exposes systems to hackers, including autonomous AI agents.
Senate debate on Bill C-22's lawful-access powersBill C-22 second reading: Dhillon, Simons and Woo speechesWhy this label?
The case concerns Bill C-22 Part 2's proposed mandatory capabilities, metadata retention and safeguards. Simons criticizes the security consequences of compulsory capabilities.
This label describes the statement's response within the context above.
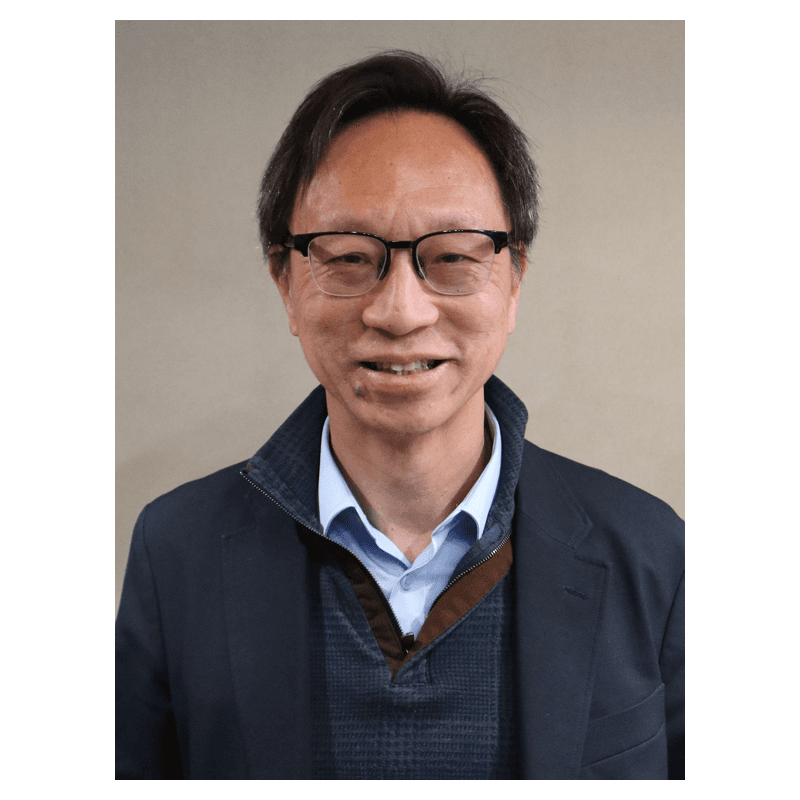
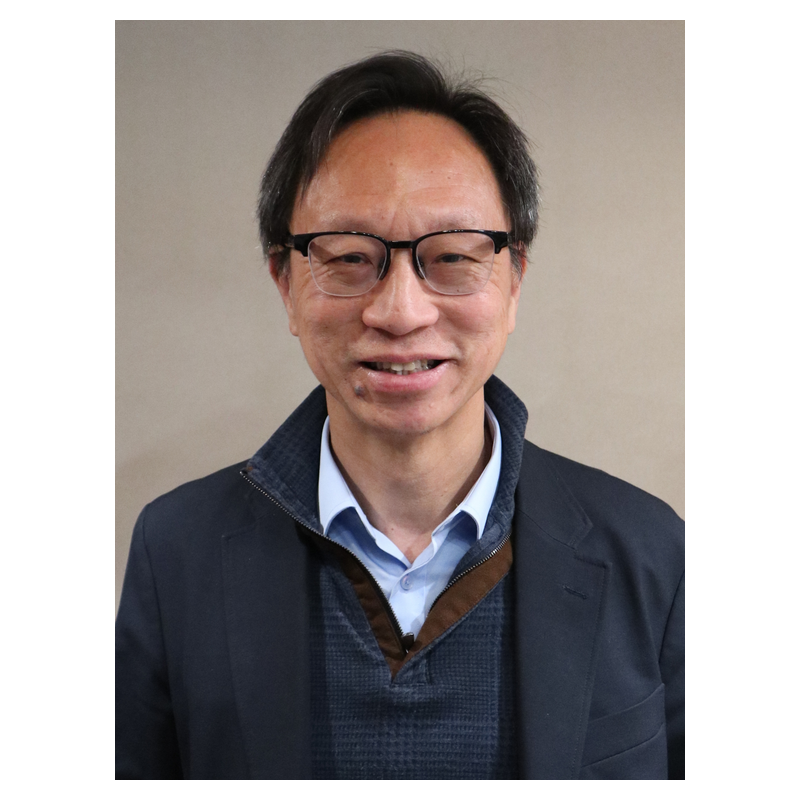 Yuen Pau WooCanadian senator for British ColumbiaDirectly involved
Before this statement
Woo says the government must demonstrate that investigative benefits justify the additional risks. He says he has serious reservations about passing the bill in its present form.
"I do not believe it has yet done so."
CondemnedCase context: Canada's Bill C-22: Dhillon backs lawful access; Simons warns of security risks
Full statement and sources
Woo says the government has not shown that investigative benefits justify the added risks and urges committee study and substantial amendments.
After the statement
He calls for committee study and substantial amendments, and says he is not confident the bill can pass as it exists without increasing risks to privacy, data and businesses.
Senate debate on Bill C-22's lawful-access powersBill C-22 second reading: Dhillon, Simons and Woo speechesWhy this label?
The case concerns Bill C-22 Part 2's proposed mandatory capabilities, metadata retention and safeguards. Woo criticizes the government's case for these powers in the bill's present form and urges substantial amendments.
This label describes the statement's response within the context above.
Sources
(7)
Original text
Senate debate on Bill C-22's lawful-access powers
Relevant passage: Bill C-22 second reading: Dhillon, Simons and Woo speeches
About this source
The debate contains competing evaluations of capability obligations, metadata retention, cybersecurity and oversight.
- Published
- Accessed
Original text
Senate of Canada: Progress of legislation, 1st Session, 45th Parliament
Relevant passage: Government bills (House of Commons): C-22
About this source
The Senate's progress table, dated October 22, 2026, records first reading of Bill C-22 in the Senate on June 18, 2026 and second reading on October 22, 2026, with referral to the National Security, Defence and Veterans Affairs committee. It lists no committee report, third reading or royal assent for the bill.
- Author
- Senate of Canada
- Published
- Accessed
Original text
LEGISinfo: Bill C-22 (45th Parliament, 1st Session), An Act respecting lawful access
Relevant passage: Bill status; House of Commons and Senate stages; publications
About this source
LEGISinfo records first reading in the House of Commons on March 12, 2026, committee amendments and third reading on June 18, 2026, and Senate second reading and referral to the Standing Senate Committee on National Security, Defence and Veterans Affairs on October 22, 2026. When we checked it on October 24, 2026, the bill was at consideration in committee in the Senate, the committee stage showed no activity, and the bill had not received royal assent.
- Author
- LEGISinfo
- Accessed
Original text
Bill C-22, Lawful Access Act, 2026, as introduced in the House of Commons
Relevant passage: Part 2, clause 41: new Act ss. 2(1) (systemic vulnerability), 5(2)(d) and 7(1)
About this source
As introduced, Part 2 let the federal cabinet require core providers to retain categories of metadata for up to one year (section 5(2)(d)). It defined a systemic vulnerability as one that creates a substantial risk of unauthorized access, and it set no maximum length for ministerial orders (section 7(1)). The House of Commons public safety committee amended these provisions before the House passed the bill on June 18, 2026.
- Author
- House of Commons of Canada
- Published
- Accessed
Original text
Bill C-22, Lawful Access Act, 2026, as passed by the House of Commons
Relevant passage: Part 2, clause 41: new Act ss. 2(1)-(4), 3, 5(1)-(6), 7(1)-(5), 24(2.1) and schedule; clauses 47 and 48
About this source
Part 2 of the House-passed text enacts the Supporting Authorized Access to Information Act. Section 5(2) lets the federal cabinet set capability and metadata-retention obligations for core providers, with retention capped at six months. Section 7 lets the Minister of Public Safety order any electronic service provider to meet such obligations for up to two years, once the Intelligence Commissioner approves the order. Sections 5(5), 7(5) and 24(2.1) excuse compliance that would introduce a systemic vulnerability, and section 2(4) limits decryption obligations.
- Author
- House of Commons of Canada
- Published
- Accessed
Analysis
Robert Diab examines Bill C-22 after the Commons amendments
Relevant passage: Encryption and metadata-retention sections
About this source
Diab considers the amended text and questions whether its safeguards resolve privacy concerns.
- Author
- Robert Diab
- Published
- Accessed
Official statement
Canada explains amendments and safeguards in Bill C-22
Relevant passage: Part 2; safeguards; metadata retention
About this source
The government defends the amended framework, including a six-month maximum and separate legal authorization to obtain information.
- Accessed
Share or embed this case
The embed keeps its attribution link to The Dispute Index. Credit the image to The Dispute Index and link to the case page.
Cite this record
- Publisher
- The Dispute Index
- Title
- Canada's Bill C-22: Dhillon backs lawful access; Simons warns of security risks
- First published
- Last updated
- Permalink
- https://disputeindex.com/cases/canada-bill-c22-lawful-access-metadata-encryption
The Dispute Index. "Canada's Bill C-22: Dhillon backs lawful access; Simons warns of security risks". First published: 2026-10-25. Last updated: 2026-10-25. https://disputeindex.com/cases/canada-bill-c22-lawful-access-metadata-encryption